The first Glass Firewall conference
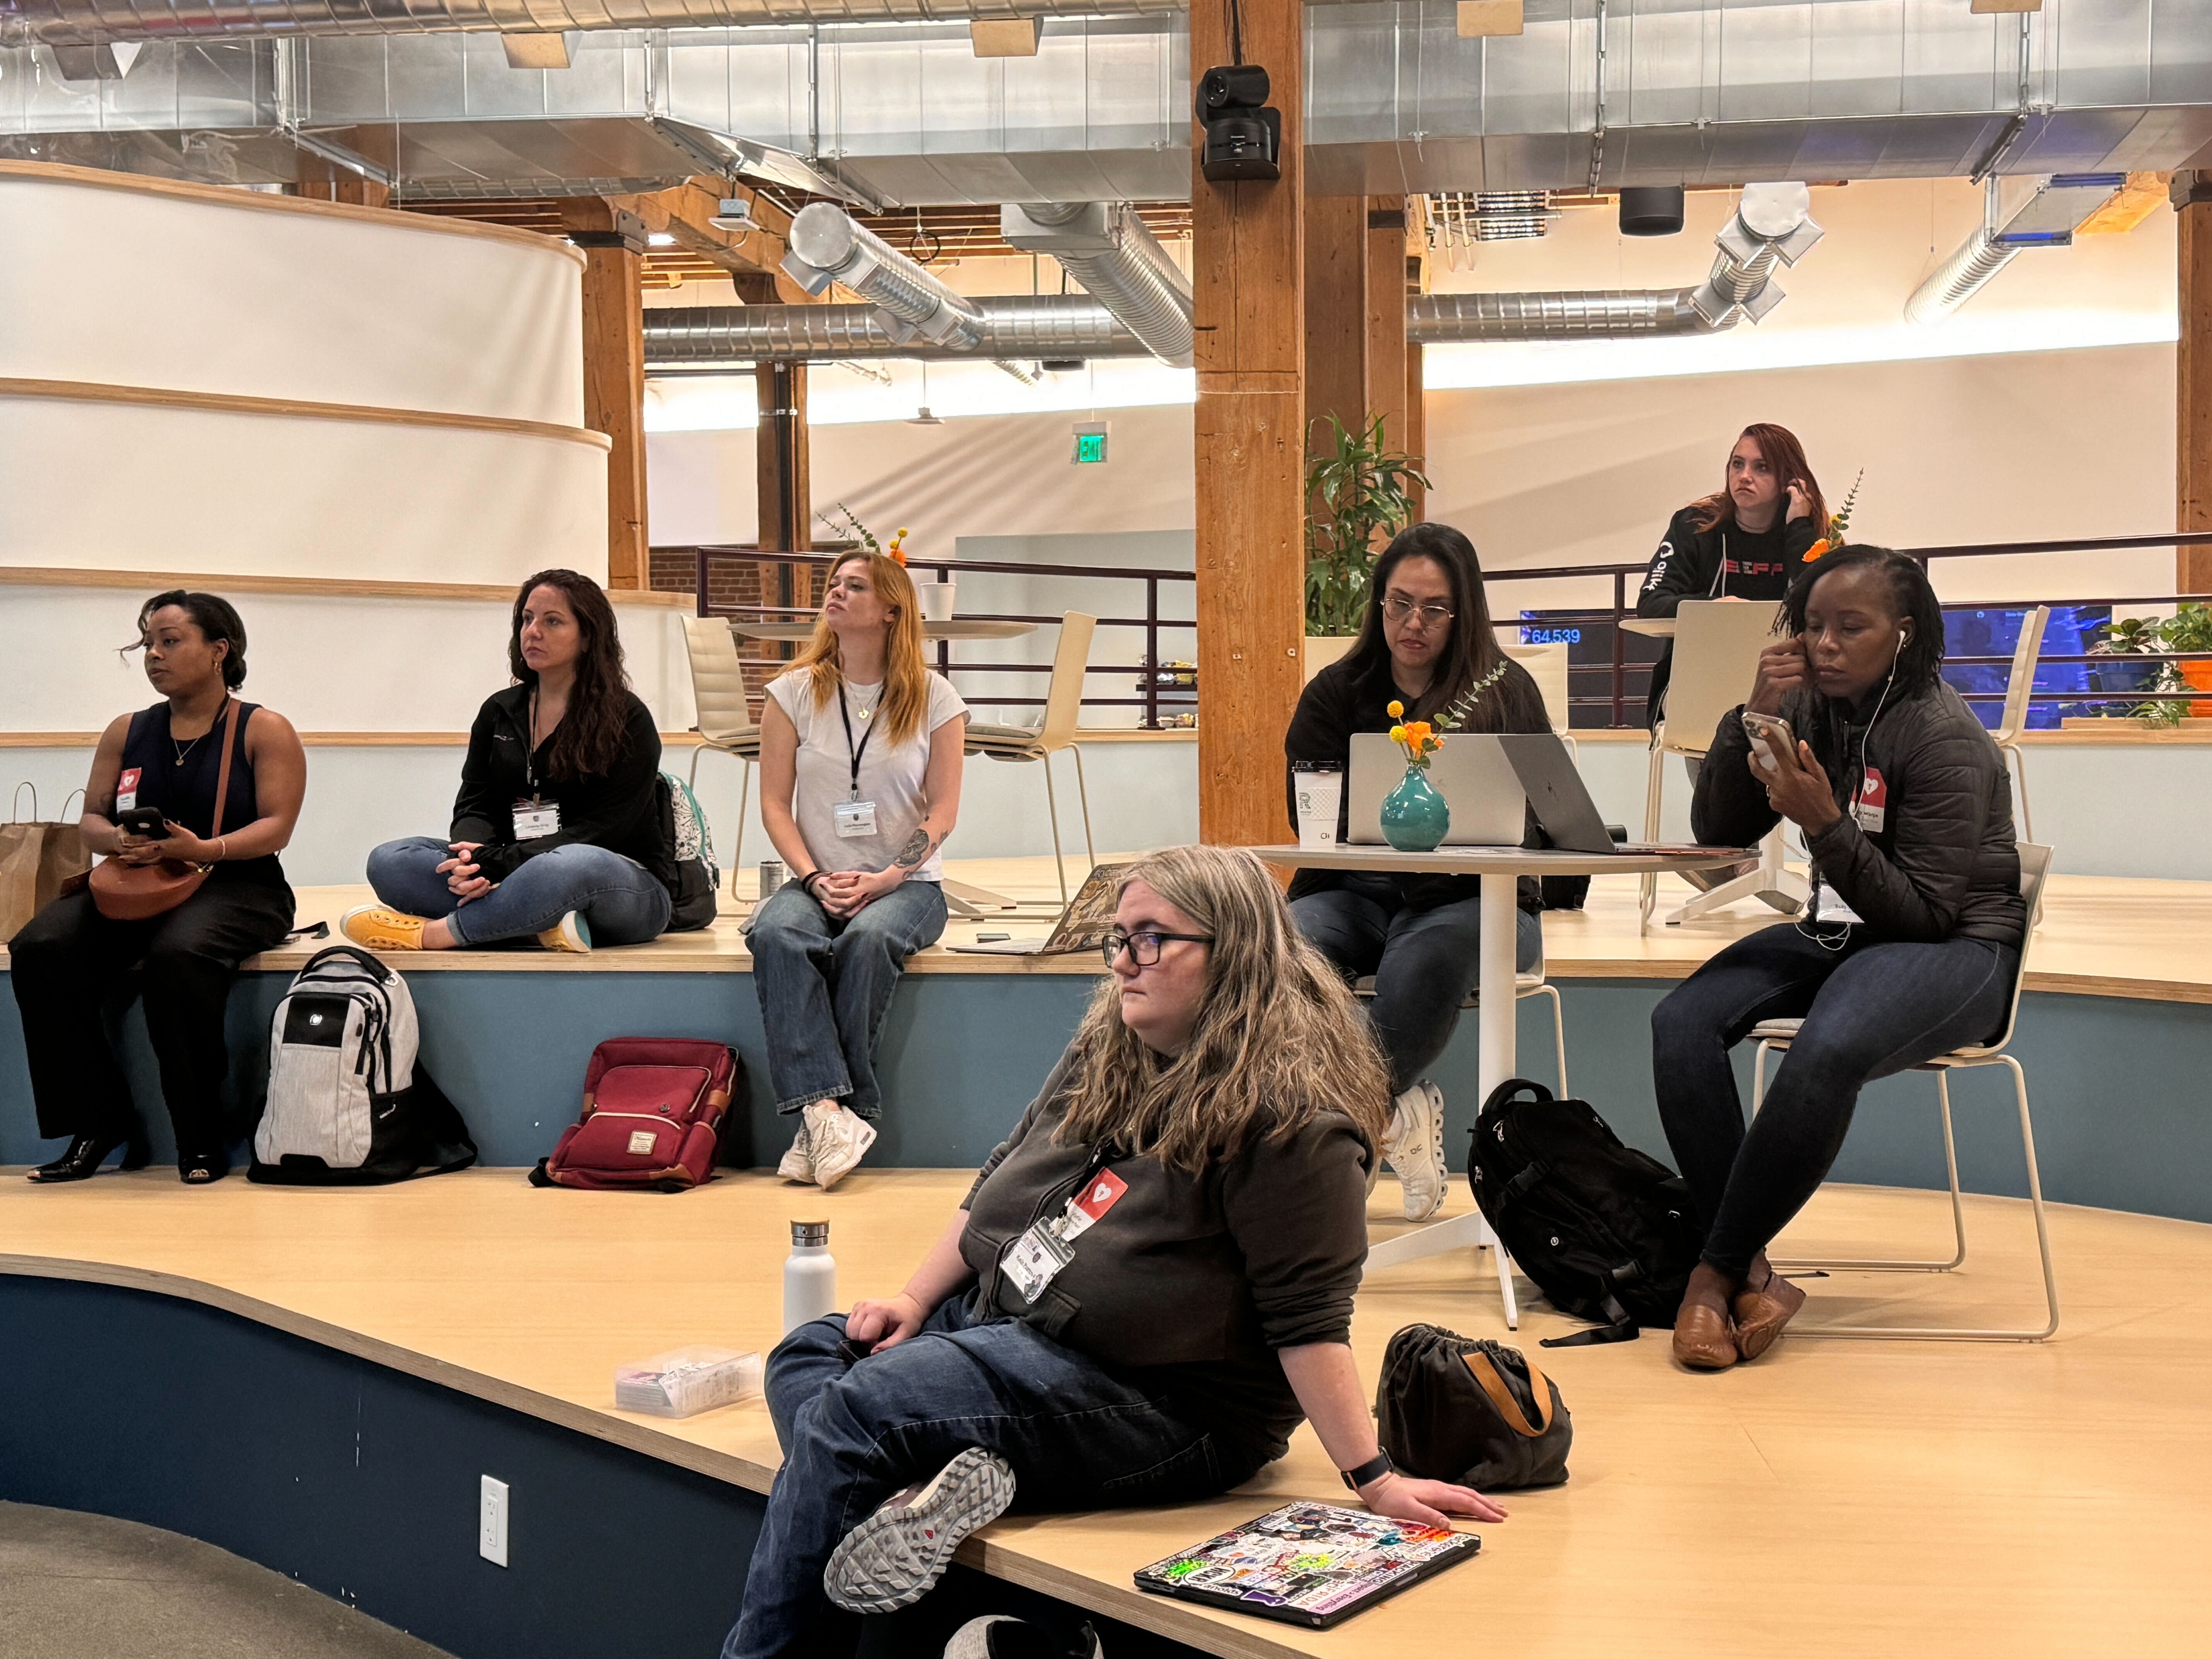
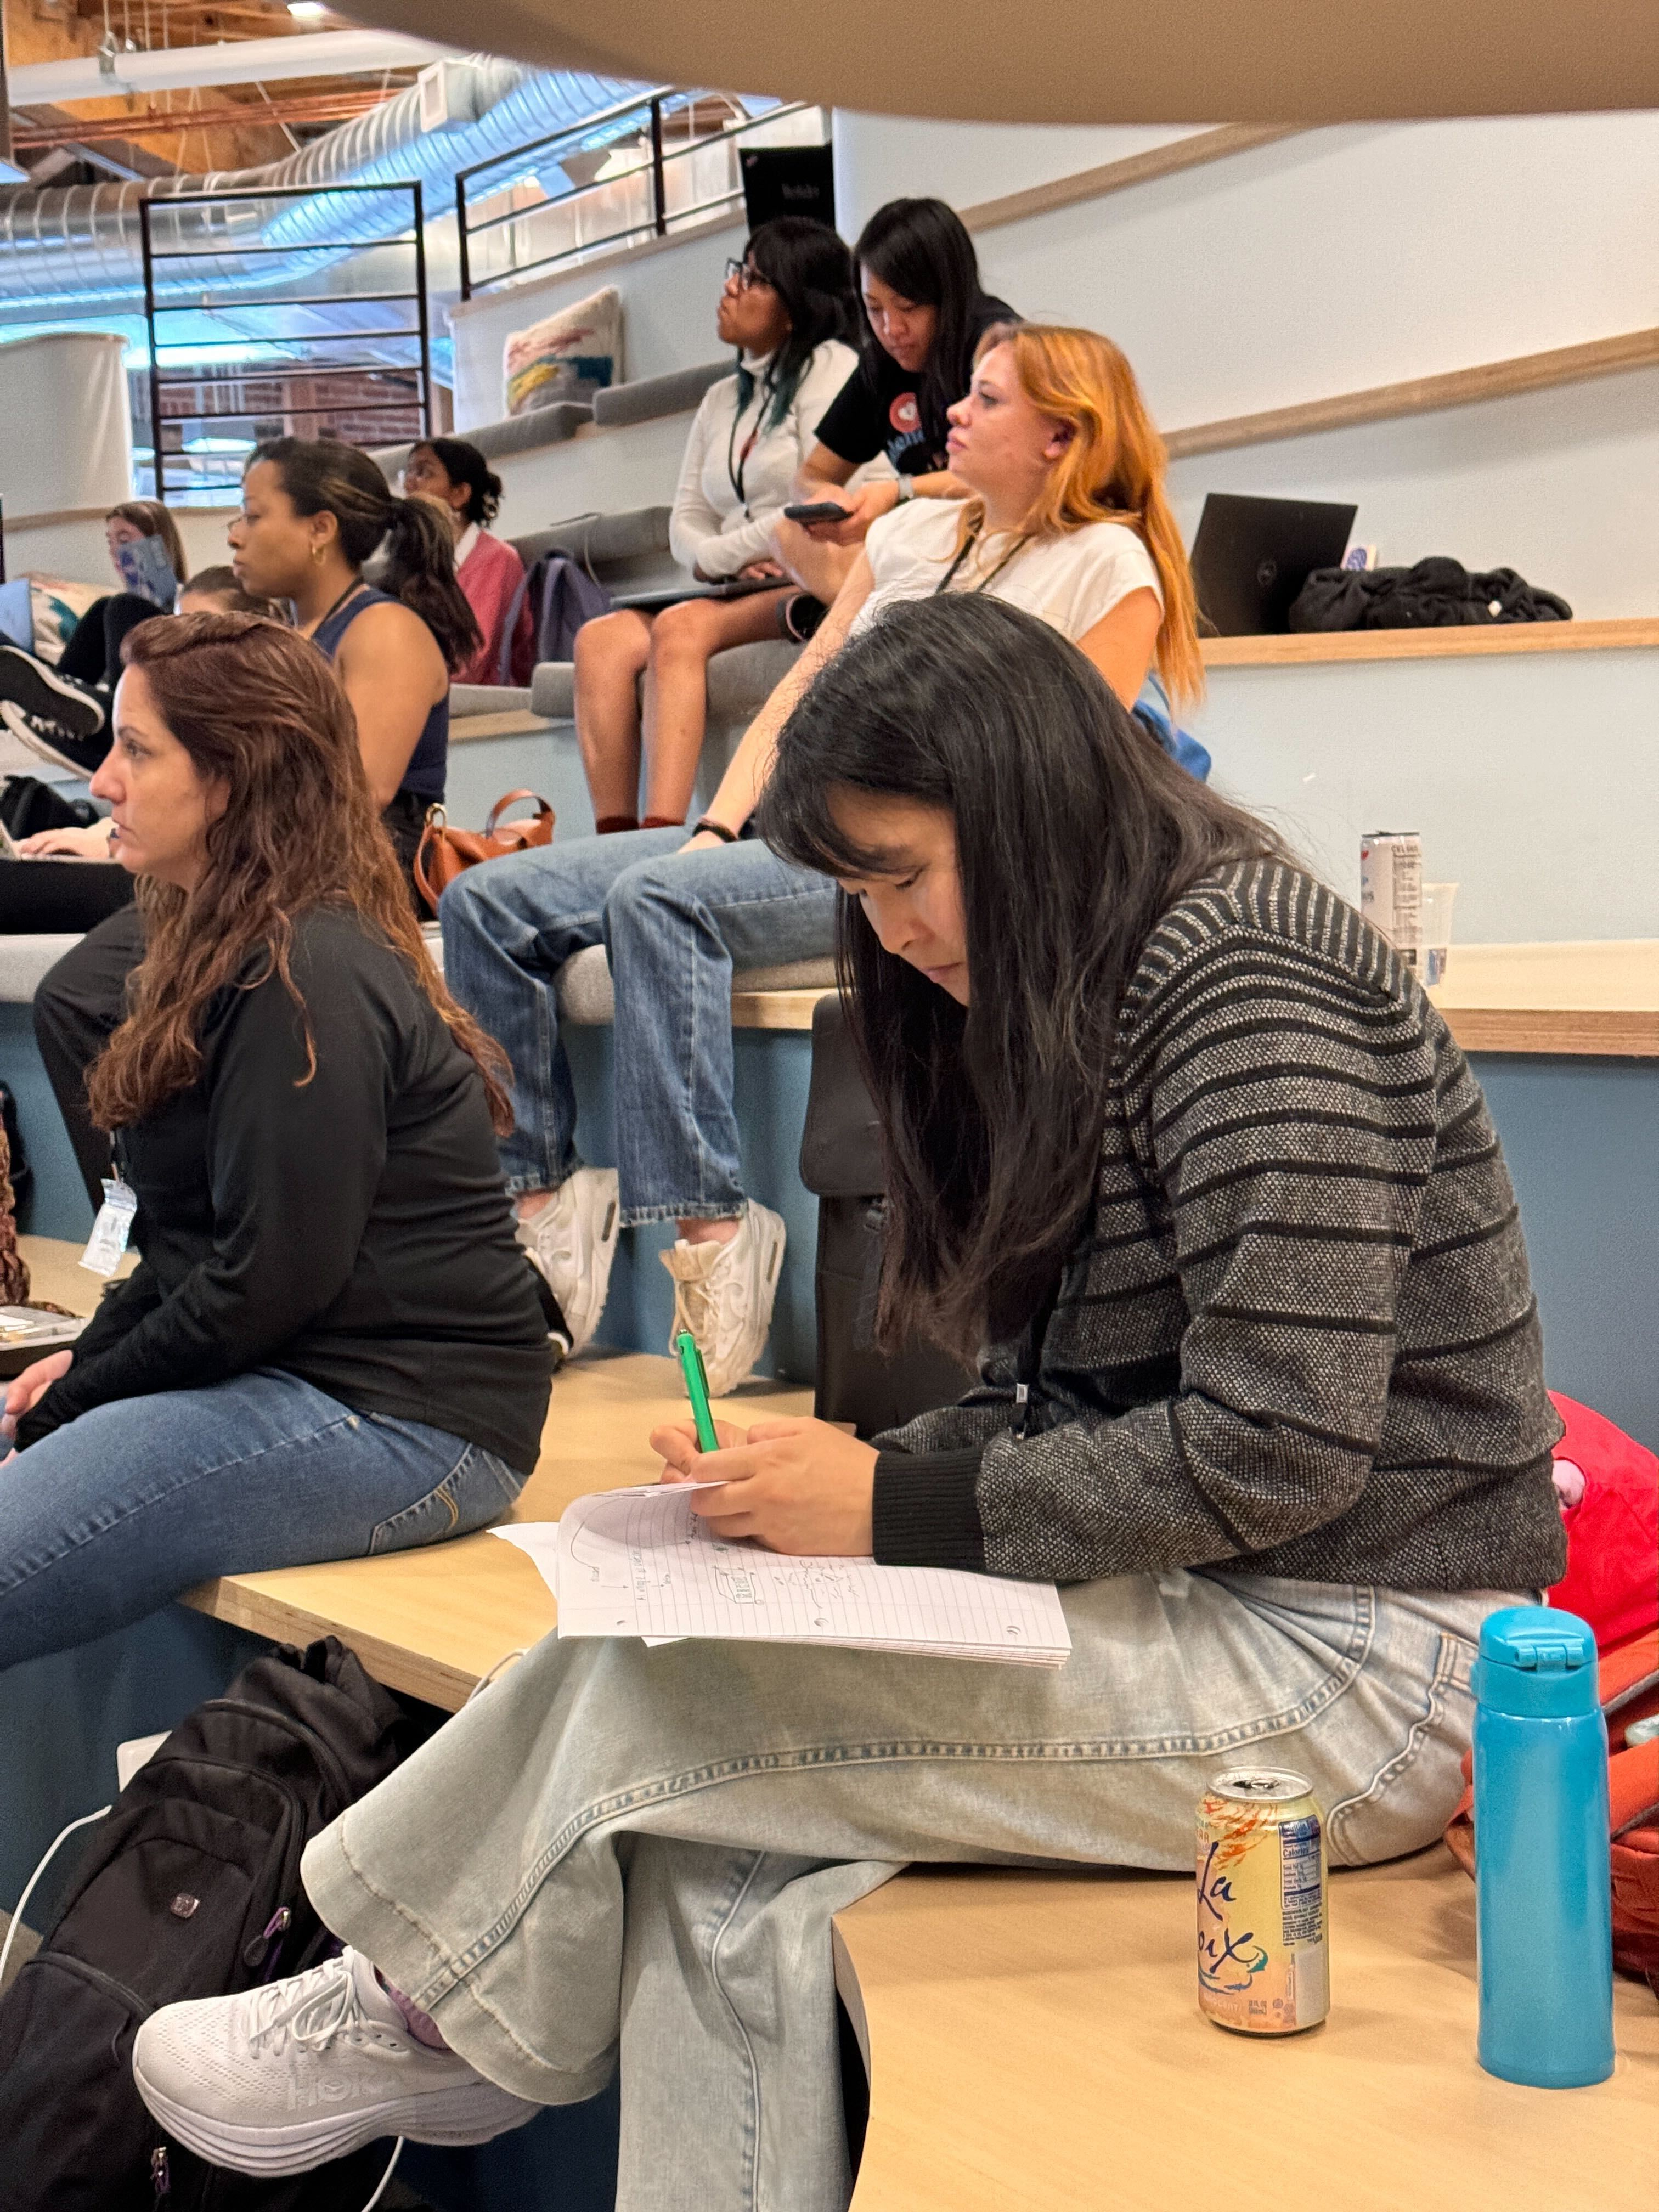
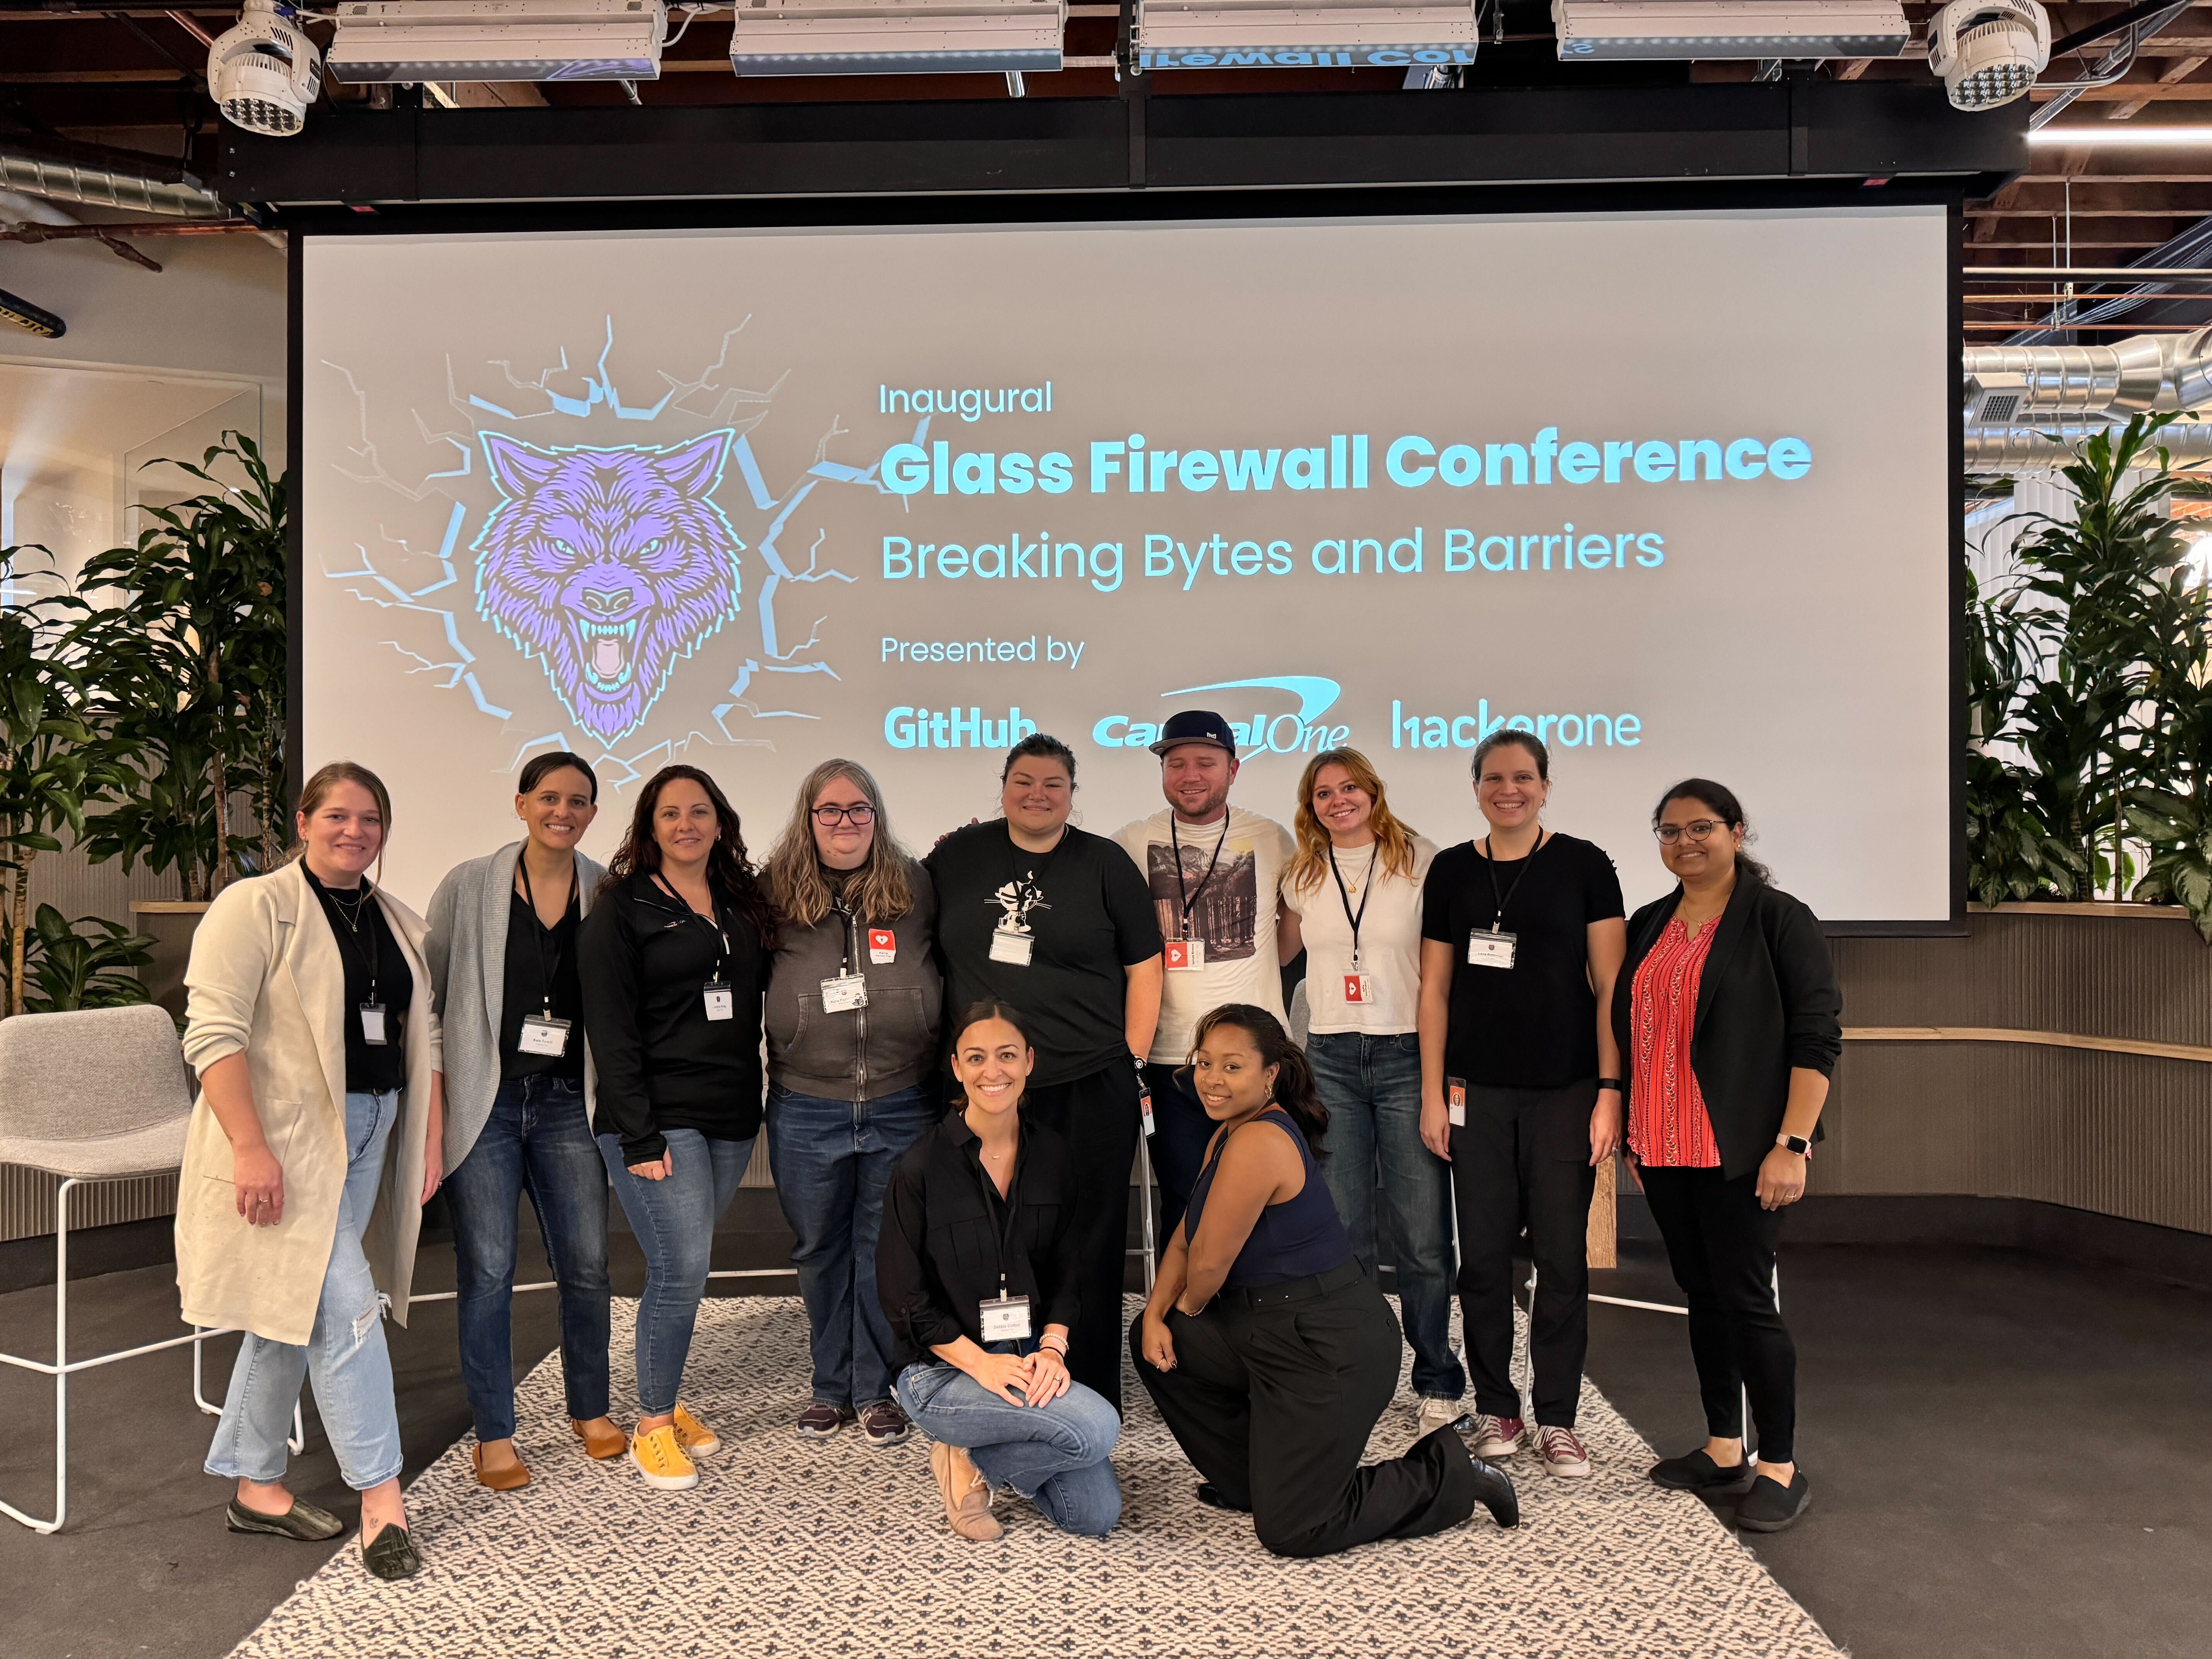
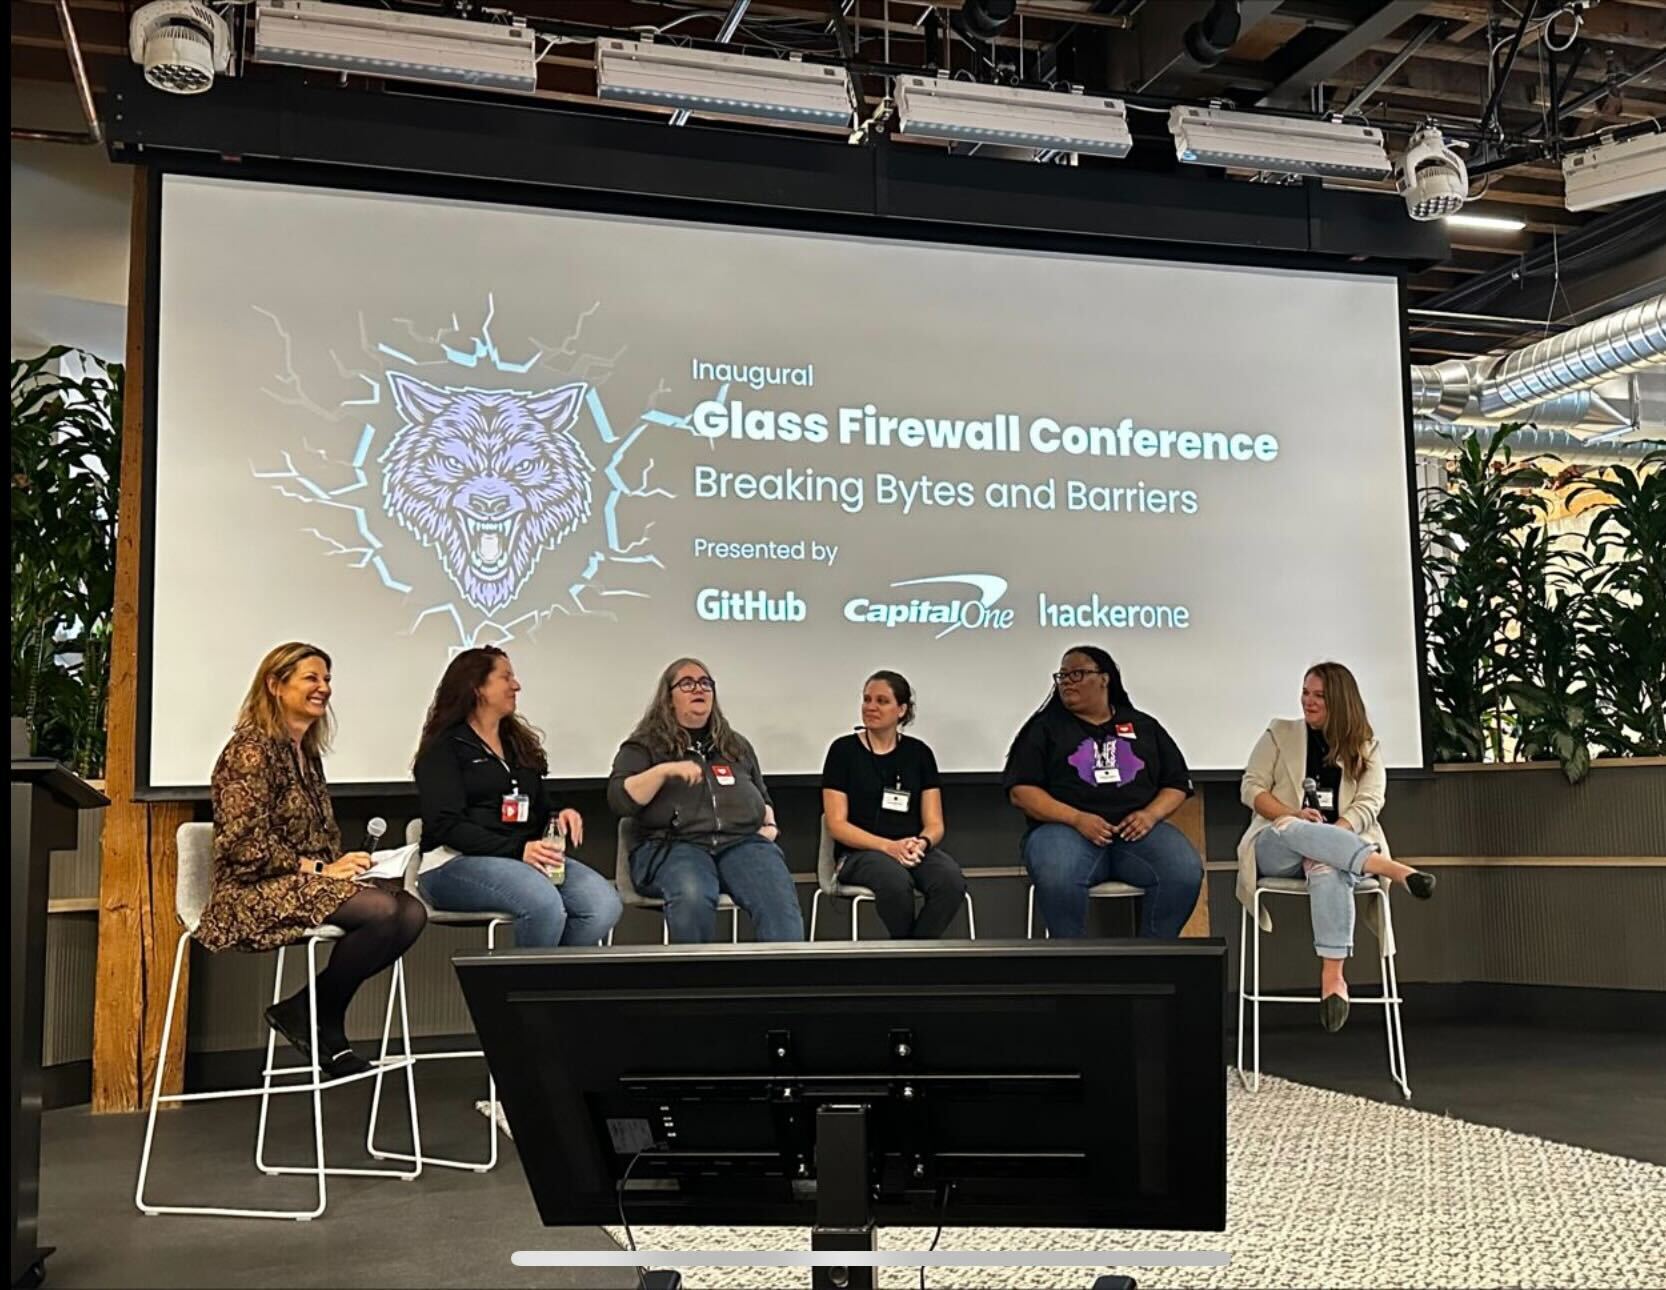
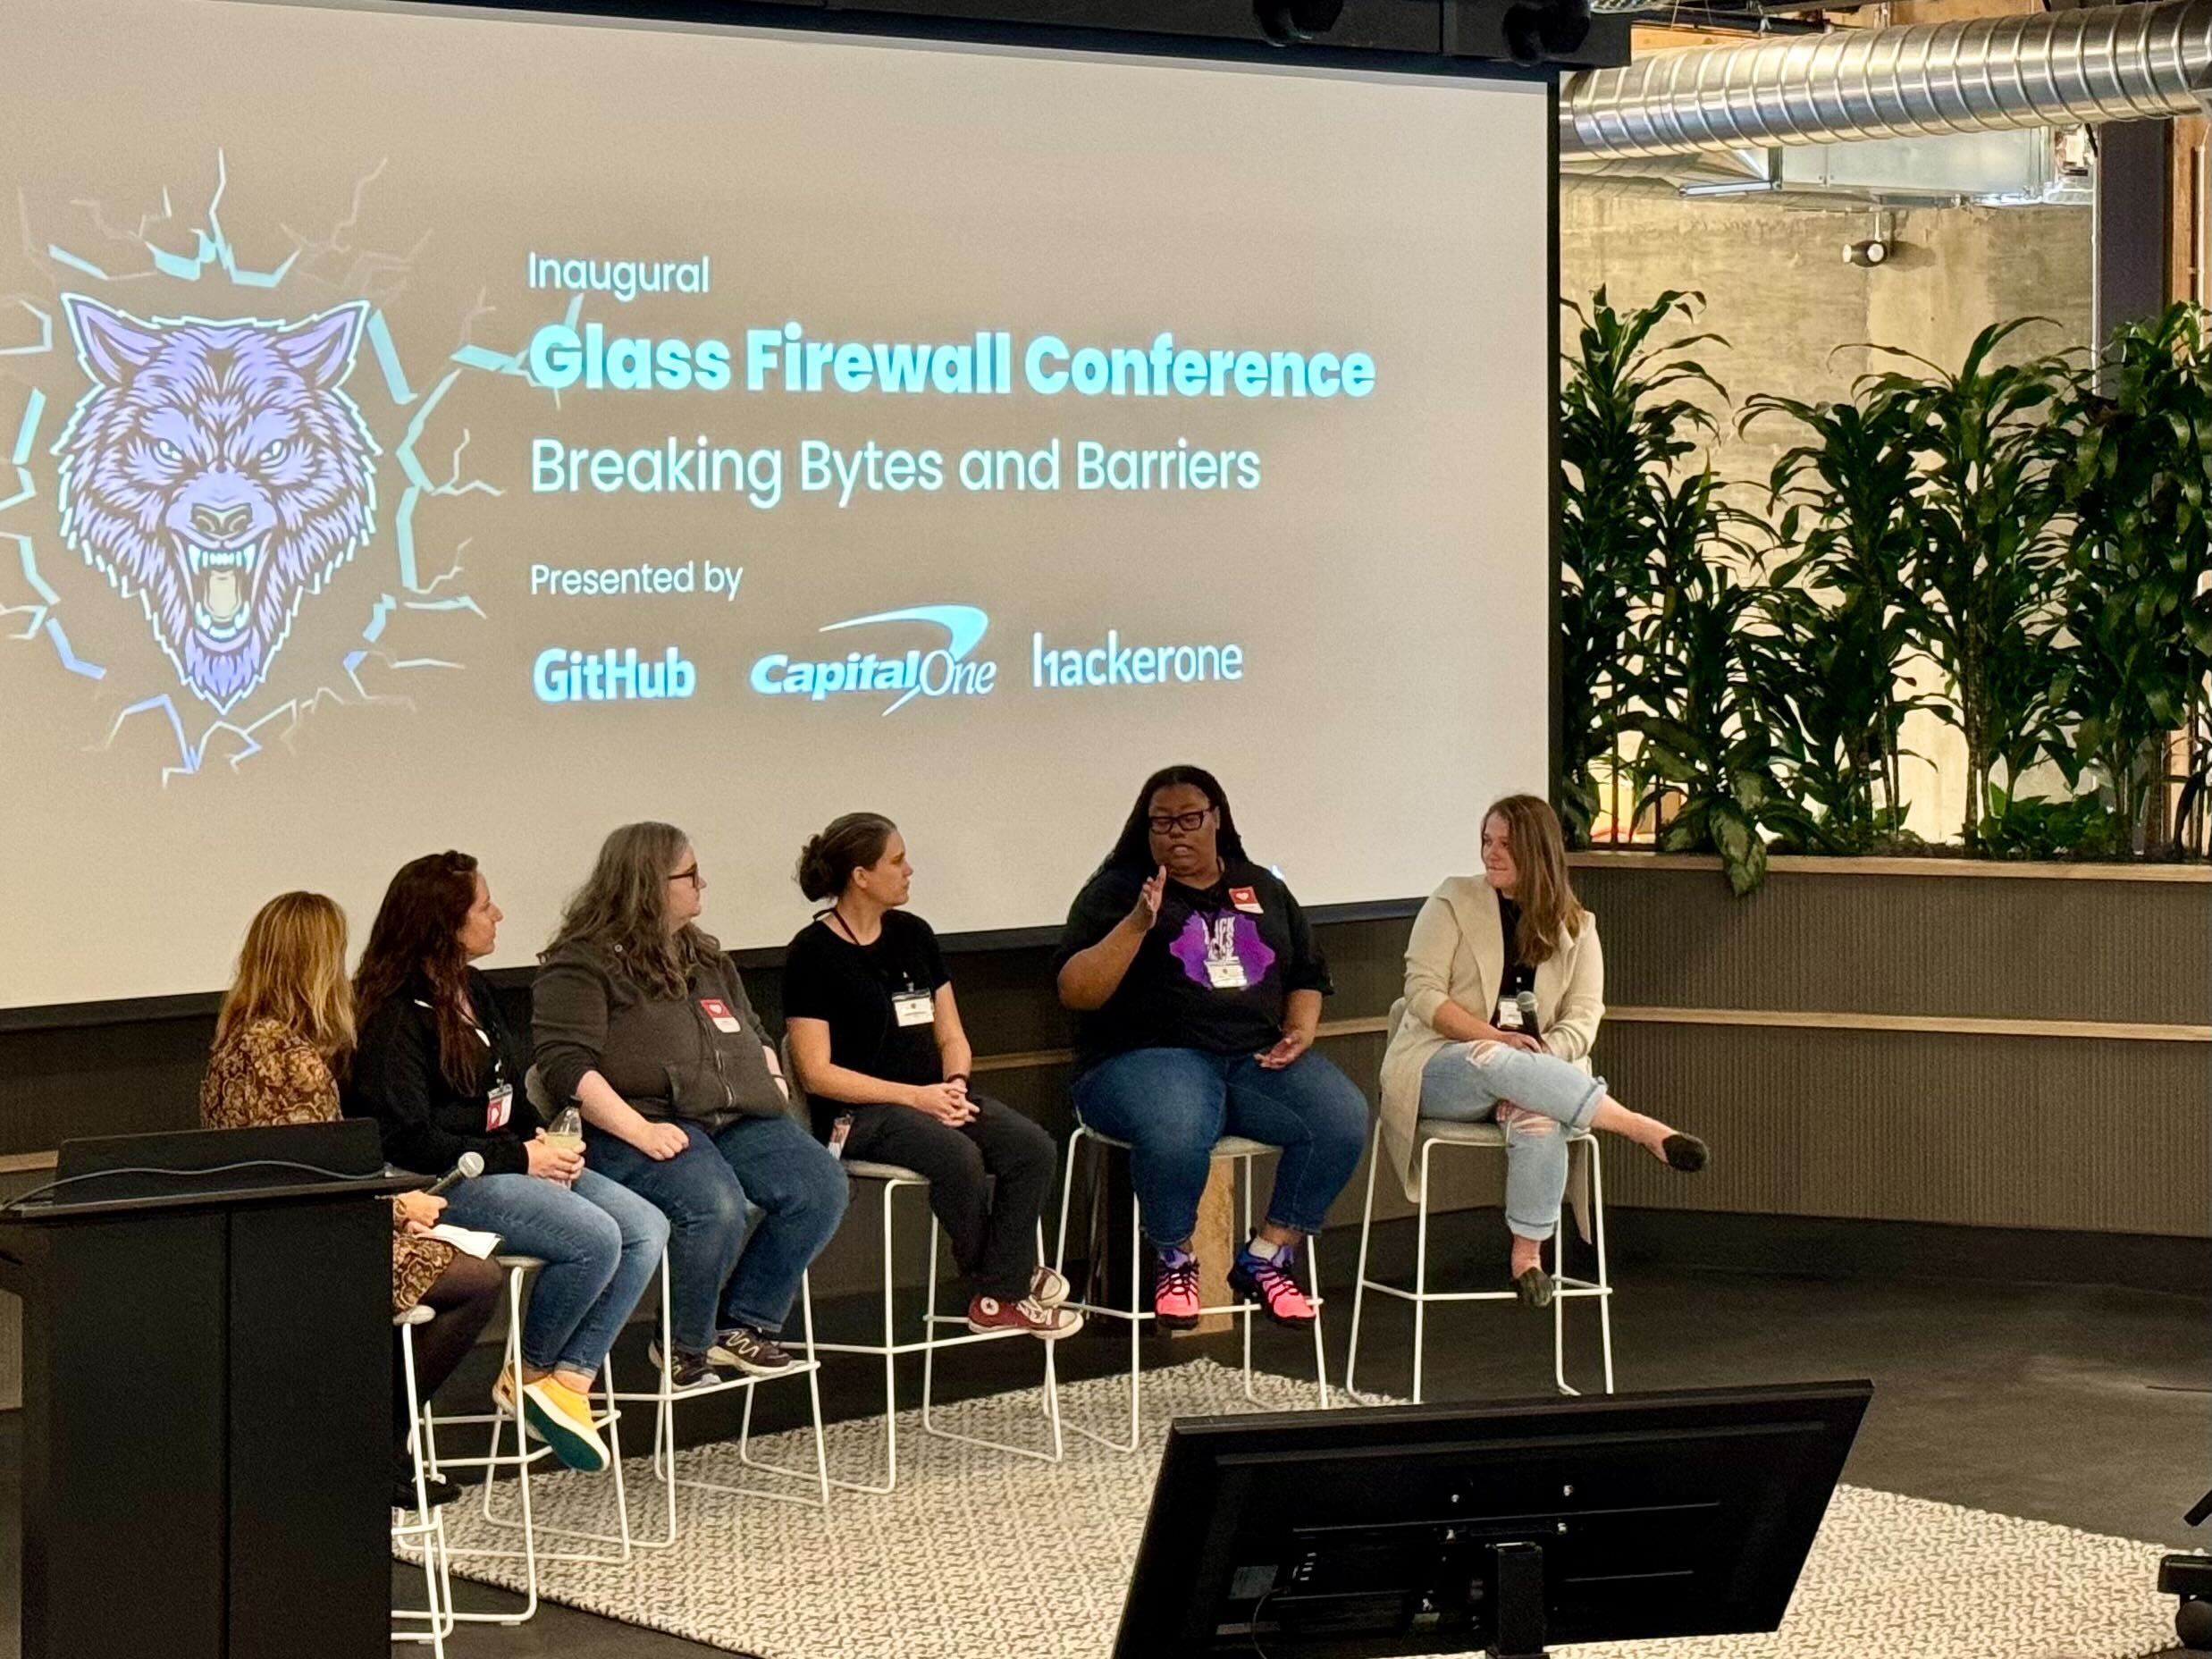
The inaugural Glass Firewall Conference brought women together at GitHub headquarters in San Francisco, with a virtual option for attendees joining from elsewhere. About 60 people came to the free event created by Capital One, GitHub, and HackerOne, and for many of them it was the first time they had been in a room full of women learning security together.
The program was built for beginners and early-career professionals, with sessions on HackerOne, web vulnerabilities, reconnaissance, Burp Suite, and a web application capture-the-flag challenge. It created a space where people could ask questions without feeling like they had to already know the answers.
Why the event is needed
Glass Firewall began because women are consistently underrepresented in bug bounty programs and security research, and the path into ethical hacking often feels difficult to enter without years of prior experience. The first conference made that path feel more open: attendees could learn the basics, meet women already working in the field, and start building a network of people who understood what it was like to begin from scratch.
It also set the tone for the events that followed: teach practical skills, share honest career stories, and create a place where people can practice, connect, and belong.
Community support
Community partners included the Women’s Society of Cyberjutsu, Black Girls Hack, Women in CyberSecurity, and Women in Security and Privacy. They helped spread the word and connected attendees with other groups supporting women in security.
Continue exploring: Read the HackerOne conference recap or view the original event details.
Program highlights
Web vulnerability foundations
An introduction to XSS, SQL injection, CSRF, and why web security matters.
Reconnaissance practice
Participants learned how researchers gather information, choose a direction, and turn observations into testable ideas.
Burp Suite workshop
A guided introduction to the tools used to inspect and understand web traffic.
Capture the flag
Participants used what they learned in a web application security challenge.
Photos from 2023